
Cyber risk management for fleet and shore operations.
STORM GRC is a maritime cyber security compliance platform that gives DPAs, Company Security Officers and IT Superintendents one workspace to manage cyber risk across fleet and shore — built around IMO Resolution MSC.428(98), IACS UR E26/E27, BIMCO guidelines and the NIS2 maritime scope.


Maritime cyber security stopped being an IT topic in 2021. It’s been an SMS topic ever since.
Maritime cyber requirements continue to expand through IMO resolutions, class requirements and EU regulation. Each new requirement builds on controls and processes that operators are already expected to have in place.
IMO 2021
From the first annual DOC verification after 1 Jan 2021, cyber risk must be addressed in the Safety Management System under the ISM Code.
IACS UR E26 / E27
For vessels contracted from 1 July 2024, class societies require demonstrable cyber resilience for vessels and the systems onboard them.
NIS2 reaches the port
Port operators, terminal handlers and many maritime service providers now fall under NIS2’s essential-entity obligations.
Port State Control
Port State Control regimes are increasingly checking cyber documentation as part of ISM-related inspections — a deficiency here is a hold.
One platform. Shore and fleet.
Most cyber tools were built for an office. STORM GRC is built for an operator that has an office, a fleet, and a regulator that doesn’t separate the two.
Shore
Run your office ISMS the way auditors expect: asset register, risk treatment plan, policies and procedures, internal audits, awareness — all unified in STORM GRC.
- ISO 27001-aligned ISMS for head office
- GDPR & DPIA workspace for crewing & HR data
- Vendor & agency security assessments with BitSight ratings
- Awareness training and phishing simulations for shore staff
- Incident, non-conformity and corrective-action registers
Fleet
Manage cyber risk at vessel level the way the Safety Management System manages every other risk: documented, attributable, auditable.
- Per-vessel asset register (IT, OT, comms, navigation)
- Cyber risk assessment per vessel type & trade
- Cyber procedures aligned to ISM Code structure
- Cyber incident reporting via your existing SMS
- Pre-PSC inspection self-check, runnable before each call
Every framework a DPA, MTM or auditor will name.
STORM GRC’s maritime configuration is pre-mapped to the regulations and guidelines that apply to commercial shipping. You don’t translate generic ISO 27001 controls into the language of the ISM Code — STORM GRC does that for you.
What your DPA actually opens on Monday.
A risk register, treatment plan and document library configured for shipping — so the DPA, CSO and Tech team aren’t translating the latest BIMCO guidance into your own format every time something changes.
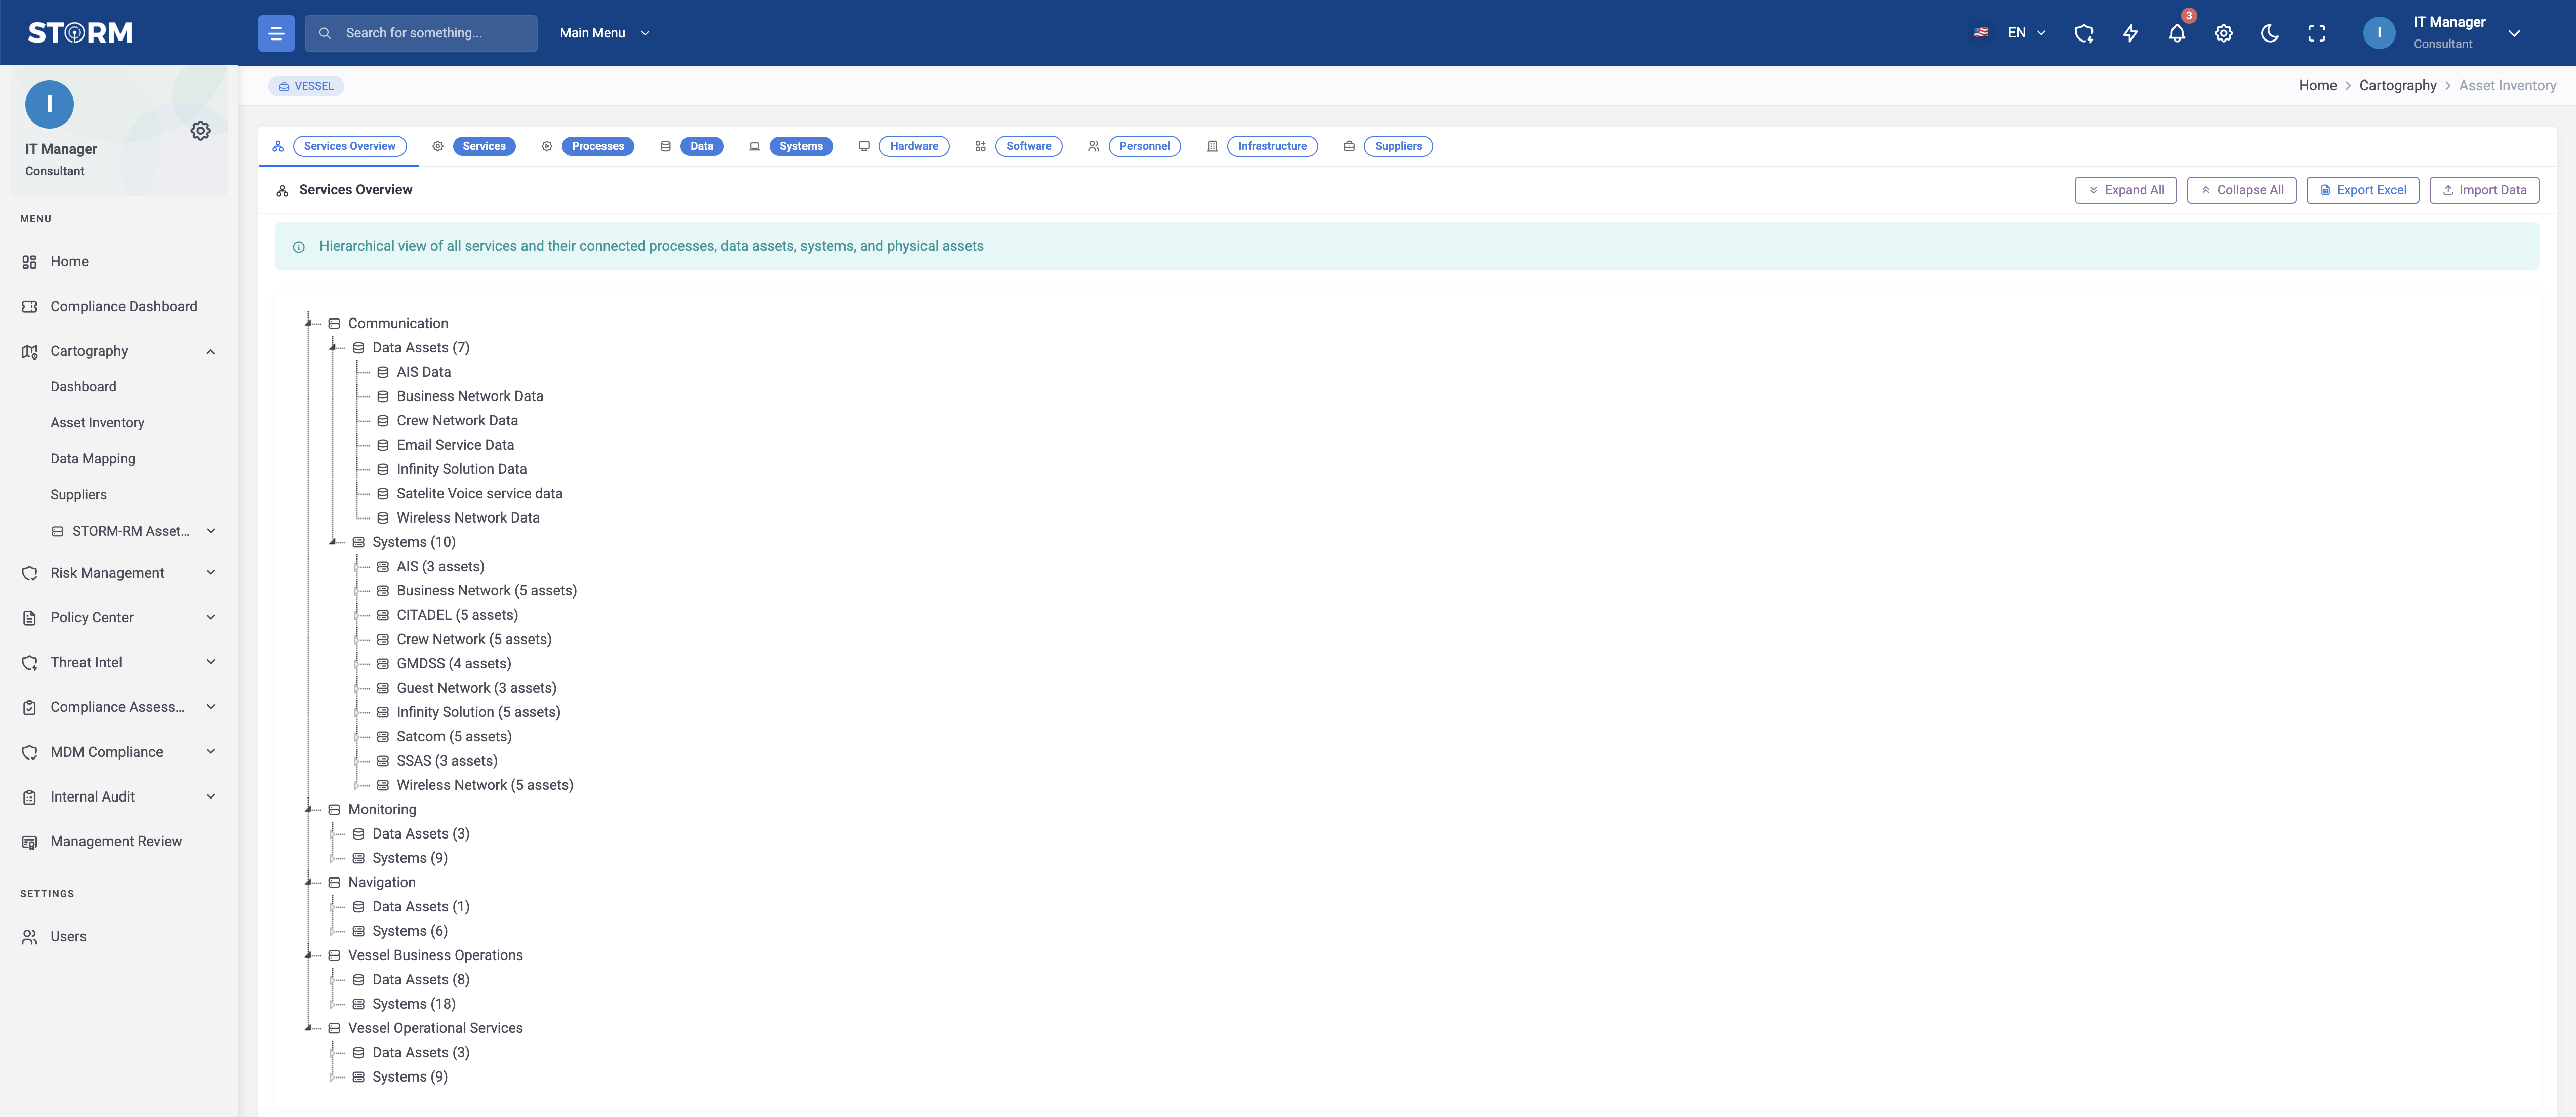
Per-vessel risk register
Each vessel has its own asset inventory and risk register, rolled up to the fleet view your management board wants to see.
Cybersecurity-ready documentation
Cyber Security Management System and Vessel Cybersecurity Manuals written in the structure and language of the Safety Management System.
Pre-PSC self-check
A short, captain-friendly checklist that mirrors what Port State Control inspectors are now asking for — runnable before each call.
From kickoff to audit-ready in 90 days.
A typical mid-size operator (15–40 vessels, shore office) hits audit-ready cyber posture within one quarter. Larger operators or new builds with IACS UR E26 obligations run a longer programme — but the first 30 days look the same.
Shore foundation
- STORM GRC tenant provisioned and configured for maritime
- Shore office asset inventory complete
- Initial cyber risk register live, mapped to ISM
- Stakeholders (DPA, CSO, IT, Tech) onboarded
Fleet-wide assessment
- Per-vessel cyber risk assessment delivered
- Vessel-level treatment plan with owners
- Cyber procedures integrated into SMS
- Awareness rollout to seafarers begins
Audit-ready
- Internal audit completed and reported
- Management review pack signed off
- Pre-PSC self-check rolled out to fleet
- External audit / DOC verification supported
STORM GRC helps maritime operators centralise cyber risk management, vessel-level procedures, audit evidence and compliance workflows into one operational workspace aligned with maritime regulations and Safety Management System requirements.
Operational focus
Maritime cyber security compliance — questions from Maritime IT teams.
If your question isn’t here, the answer is a 30-minute call — usually faster than email.
Does the vessel side need bandwidth to use STORM GRC?
Will STORM GRC disrupt our existing SMS?
We have an existing ISO 27001 ISMS for the office. Do we start over?
Does STORM GRC cover IACS UR E26 / E27 for new builds?
Are we caught by NIS2?
How does the integration with our security stack work?
ICT PROTECT holds internationally recognised certifications across quality, security and assurance.
Walk us through your fleet. We’ll walk you through STORM GRC.
A practical discussion with someone experienced in DOC verification and maritime cybersecurity assessments. You receive a short written summary of the main gaps identified against IMO MSC.428(98) and IACS UR E26/E27.
EU-based team. Genuine maritime references on request.